
Penetration Testing Remediation: How to Fix Findings & Retest


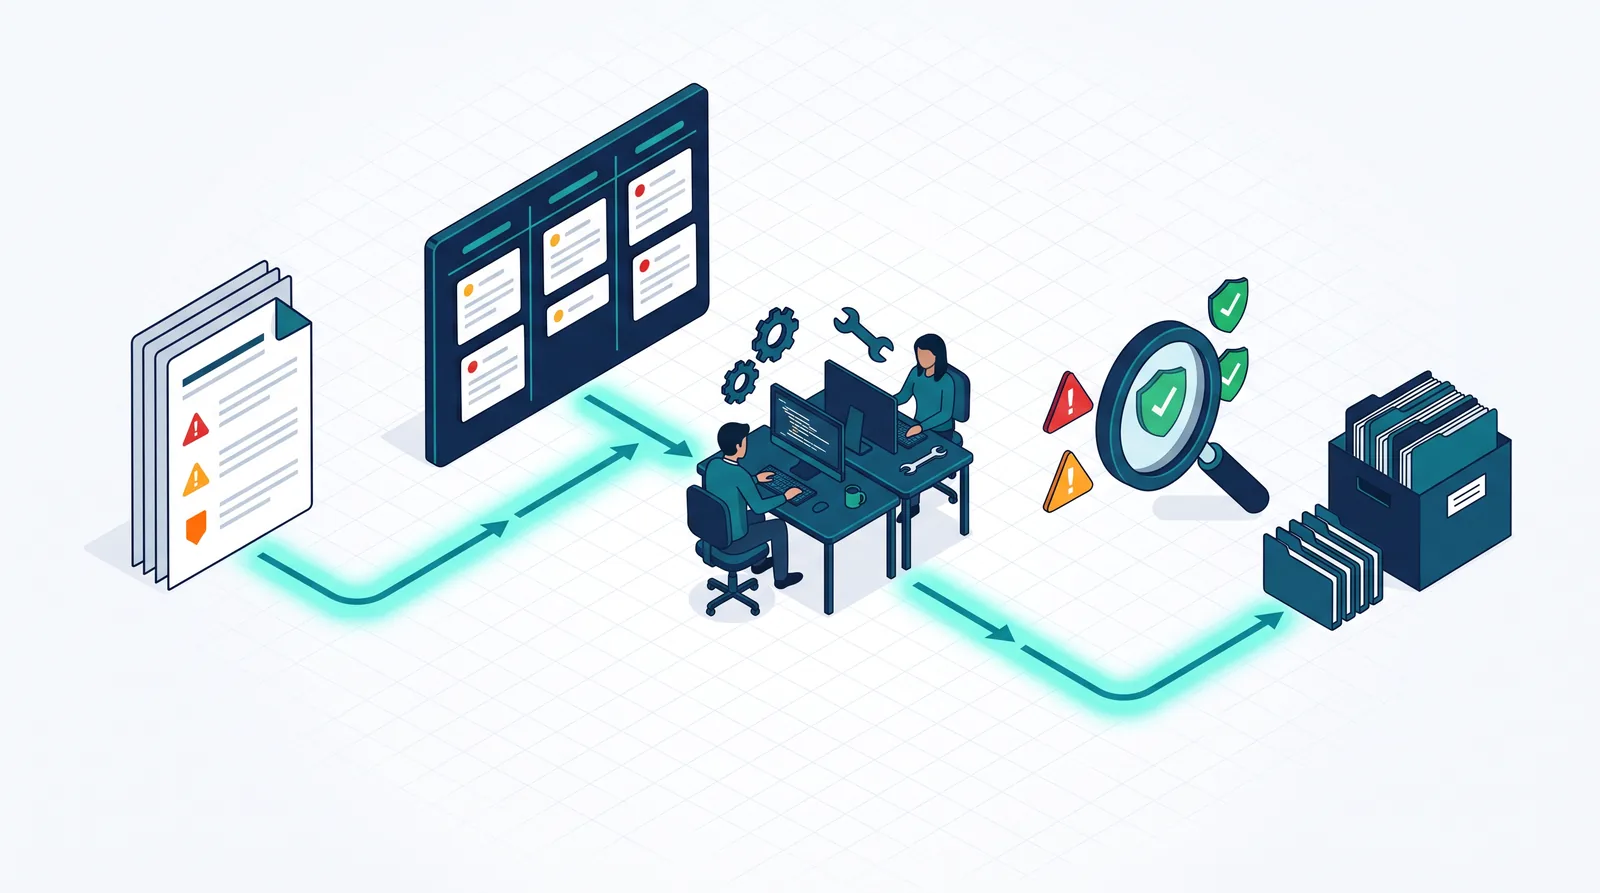
Quick answer: Penetration testing remediation is the process of fixing the vulnerabilities a test finds and proving they are fixed. The steps are to triage by risk, assign owners and due dates, fix or formally accept each finding, request a retest and keep evidence. Without remediation and retesting, a penetration test is only a list of problems.
A penetration test report does not improve security by itself. It becomes valuable when findings are fixed and verified. Yet this is the stage where many programs stall: the report arrives, the team is busy, tickets drift and six months later the same critical issue is still open when the auditor asks about it.
This guide covers penetration testing remediation end to end: how to triage, who should fix what, how long it should take, how to handle exceptions and how to retest. For testing with built-in retesting, see Privaxi's penetration testing services.
What Is Penetration Testing Remediation?
Penetration testing remediation is the work of resolving findings from a security test through patches, configuration changes, code fixes, compensating controls or a documented decision to accept the risk. It ends with verification, usually a retest, that the issue no longer reproduces.
Compliance programs treat remediation as essential. PCI DSS 11.4.4, for example, requires exploitable vulnerabilities to be corrected and the testing repeated to verify the fixes. SOC 2 and ISO 27001 auditors look for the same trail. See PCI DSS 11.4 penetration testing and ISO 27001 Annex A 8.8.
Step 1: Hold a Findings Walkthrough
Ask the testers to walk your engineers and IT staff through the report. Reproduction steps, evidence and attack chains are much easier to understand in conversation, and the testers can suggest realistic fixes. Invite developers, infrastructure owners and the person who owns the risk register.
Step 2: Triage and Prioritize
Start with the severity in the penetration testing report, then adjust for your own context:
- Exposure. Is the system internet-facing or reachable only internally?
- Data sensitivity. Does it hold regulated or customer data?
- Exploitability. Is a public exploit or a simple technique available?
- Attack chains. Does fixing one issue break a path that links several findings?
- Effort. Quick wins can be done immediately while larger changes are scheduled.
A common mistake is to fix the easiest items first and leave the dangerous ones. Sort by risk first, then batch cheap fixes alongside.
Step 3: Set Remediation Timelines
These targets are examples. Set your own in a written procedure, as auditors want to see that you defined timelines and met them.
Step 4: Assign Owners and Track Work
- One owner per finding, not a team alias.
- Create tickets in the system your engineers already use.
- Link each ticket to the report ID and the evidence.
- Add due dates based on severity.
- Review weekly until all critical and high items are closed.
- Report status to leadership and the risk owner.
Common Penetration Testing Remediation Fixes by Category
For finding examples in specific contexts, see web application penetration testing, internal penetration testing and AWS penetration testing.
When You Cannot Fix a Finding
Sometimes a fix is impossible or too costly in the short term: a legacy system that cannot be patched, a vendor product with no fix or a dependency that would break production. In those cases you have three options:
- Compensating controls. Reduce the risk another way, such as network isolation, extra monitoring or tighter access.
- Time-bound exception. Document the reason, the compensating controls, an owner, an approval and a review date.
- Risk acceptance. Leadership formally accepts the residual risk, which should be recorded in your risk register.
Auditors accept documented exceptions. They do not accept silence.
Step 5: Retest
A retest confirms that fixes work and that no new issue was introduced. Ask your provider to include one in the engagement, and plan it for after the main fixes land. A retest typically covers the critical and high findings at minimum, and often all open items.
- What the retest produces: an updated report or addendum showing which findings are closed, partially fixed or still open.
- Partial fixes: fixed in one place but not another is common, so insist on re-verification rather than assuming.
- New findings: a retest may surface related issues, which should be handled as new items.
Subscription models make retesting easier because it can be triggered on demand. See PTaaS vs traditional penetration testing and how much penetration testing costs for how retesting is priced.
Step 6: Keep the Evidence
- The original penetration test report and scope.
- The remediation log with owners, due dates and completion dates.
- Change records, pull requests, patch records or configuration screenshots.
- The retest report or addendum.
- Exception and risk acceptance approvals.
- Management review notes where relevant.
Metrics Worth Tracking
- Time to remediate by severity.
- Percentage of critical and high findings closed within target.
- Repeat findings across tests.
- Number of open exceptions and their age.
- Retest pass rate on first attempt.
These metrics show leadership and auditors whether the program is improving. Our guide to penetration testing methodology shows how testing and remediation fit into the larger cycle.
Working With Developers to Make Fixes Stick
Fixes last when developers understand the root cause. Rather than patching one endpoint, ask whether the same flaw pattern appears elsewhere and address it centrally, for example with a shared authorization layer, a safe query library or a standard input-handling module. Pair findings with secure coding guidance, add automated tests that would have caught the issue and update code review checklists. This reduces repeat findings in the next test.
Remediation in Agile and CI/CD Environments
- Convert findings into backlog items with severity, acceptance criteria and a due date.
- Reserve capacity each sprint for security fixes, so critical issues are not competing with feature work.
- Add regression tests and static or dynamic checks to the pipeline for fixed issues.
- Use infrastructure as code so configuration fixes are applied consistently and cannot silently drift back.
- Verify in staging first, then confirm in production with the testers or an on-demand retest.
Common Remediation Pitfalls
- Fixing the symptom, not the cause, which leaves similar flaws elsewhere.
- Closing tickets without verification.
- No owner, so the finding belongs to everyone and no one.
- Ignoring medium findings that combine into serious attack paths.
- Poor documentation, which makes audits painful.
- Treating the retest as optional.
Frequently Asked Questions
What is penetration testing remediation?
It is the process of fixing, mitigating or formally accepting the vulnerabilities found in a penetration test, and verifying through retesting that the fixes work.
How long should it take to fix penetration test findings?
It depends on severity. Many organizations target days for critical issues, a few weeks for high, and within a quarter for medium. Define your own targets in a written procedure.
Is a retest included in a penetration test?
Sometimes. Some providers include one retest and others charge separately, so confirm this before you sign.
What if a vulnerability cannot be patched?
Use compensating controls, document a time-bound exception with an owner and approval, and have leadership formally accept any remaining risk.
Do auditors check penetration testing remediation?
Yes. PCI DSS explicitly requires fixing exploitable findings and repeating the test, and SOC 2, ISO 27001 and HITRUST assessors look for remediation evidence.
Who is responsible for fixing penetration test findings?
Each finding should have a named owner, usually the engineering, infrastructure or security team that manages the affected system, with overall accountability held by a risk owner.
Final Thoughts
Good penetration testing remediation is simple to describe and hard to sustain: triage by risk, assign owners and dates, fix or formally accept, retest and keep the proof. Do that consistently and every test makes you measurably safer.
To work with a provider that builds retesting into the engagement, explore Privaxi's penetration testing services.
Related Articles


Secure Your Business's Future
Contact us today for a personalized consultation and see how we can tailor a security solution that fits your business needs perfectly.
