
CMMC Penetration Testing: What Defense Contractors Need to Know


Quick answer: CMMC Level 2 is built on NIST SP 800-171, which requires vulnerability scanning, risk assessments and periodic security assessments but does not name penetration testing. Level 3 draws on NIST SP 800-172, which includes penetration testing among its enhanced requirements. Many contractors still run penetration tests to prove their controls protect controlled unclassified information (CUI) and to prepare for assessment.
Defense contractors are being asked to prove, not just state, that they protect controlled unclassified information. The Cybersecurity Maturity Model Certification (CMMC) program turns that expectation into assessed requirements, and many teams are asking where penetration testing fits.
This guide explains the role of CMMC penetration testing: what the model and its underlying NIST standards actually say, why contractors test anyway, what to include and how to prepare. If you need help with the wider program, see Privaxi's CMMC compliance services.
Does CMMC Require Penetration Testing?
The answer depends on the level.
- Level 1 covers basic safeguarding of federal contract information and uses a self-assessment. It has no penetration testing expectation.
- Level 2 aligns with the 110 requirements of NIST SP 800-171 for protecting CUI. Those requirements include vulnerability scanning, risk assessments and periodic assessment of security controls. They do not name penetration testing.
- Level 3 adds a selected set of requirements from NIST SP 800-172, which are aimed at defending against advanced persistent threats. That publication includes penetration testing among its enhanced security requirements.
So CMMC penetration testing is not an explicit checkbox for most contractors at Level 2. The program's timeline and phase details have also shifted over time, so check the current status; Privaxi's articles on CMMC compliance in 2026 and Phase 2 being paused, not cancelled explain the latest picture.
Why Contractors Invest in CMMC Penetration Testing Anyway
- It validates your controls. A policy that says "least privilege" means little until a tester tries to escalate privileges.
- It supports the risk assessment and the periodic security control assessment required by NIST SP 800-171.
- It finds issues before the assessor does. A certified third-party assessor organization (C3PAO) will test whether controls are implemented and effective.
- Prime contractors ask for it. Flow-down requirements and supplier questionnaires frequently request test evidence.
- It protects the business. Defense supply chains are active targets for nation-state and criminal groups.
NIST SP 800-171 Requirements Related to Testing
Requirement numbers follow NIST SP 800-171 Rev. 2, which CMMC Level 2 currently references. Confirm the version your contract and assessment use.
What CMMC Penetration Testing Should Cover
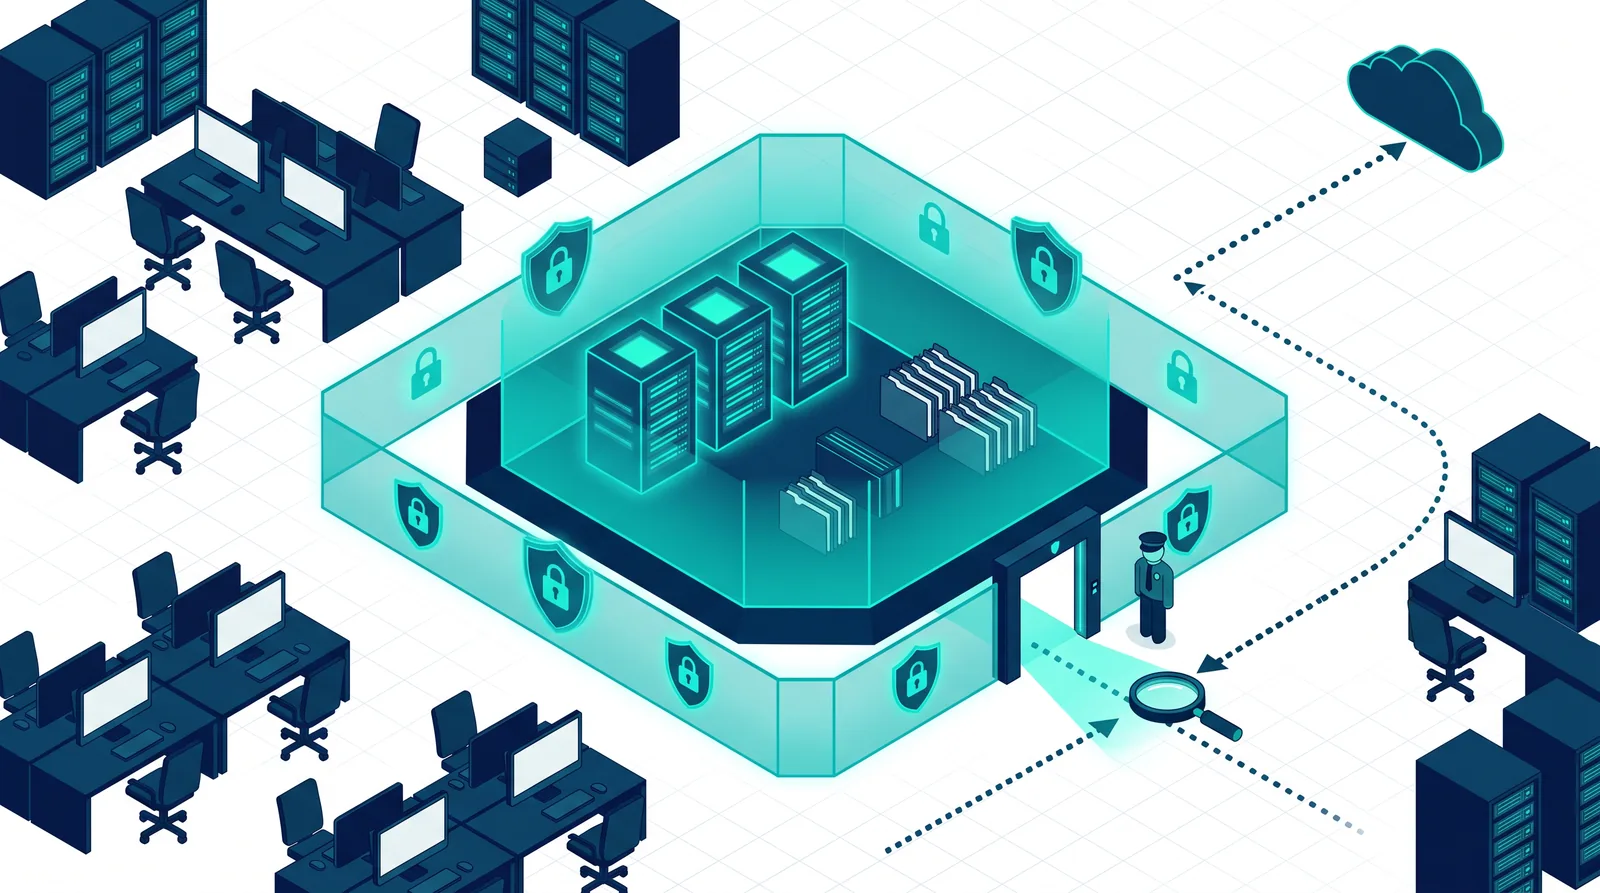
Scope your test around where CUI lives and travels. Our guide to penetration testing scope explains how to define it, and for CMMC the main areas are:
- The CUI enclave. Systems, applications and cloud tenants that store, process or transmit CUI.
- Boundary and segmentation. Whether the enclave is truly isolated from the rest of the corporate network.
- External exposure. VPN, email, portals and any internet-facing service. See external penetration testing.
- Internal paths. Lateral movement toward CUI repositories. See internal penetration testing.
- Identity and access. MFA, privileged accounts, remote access and account lifecycle.
- Cloud services. GCC High, Azure Government and other environments used for CUI, subject to their rules of engagement.
- Security monitoring. Whether attacker activity generates alerts.
CMMC Penetration Testing at Level 3
Contractors that handle the most sensitive programs may face Level 3, which incorporates selected NIST SP 800-172 requirements. Those enhanced requirements expect more rigorous and adversary-informed testing, including penetration testing that combines automated scanning with expert-led tests. Level 3 assessments are performed by the government rather than a C3PAO, and the requirements are narrower in applicability, so confirm with your contracting officer whether they apply to you.
Using CMMC Penetration Testing to Prepare for a C3PAO Assessment
- Complete a readiness assessment against the 110 requirements to find obvious gaps.
- Fix the basics first, including MFA, patching, logging and access control.
- Define the CUI boundary and document the system security plan.
- Run a penetration test scoped to the boundary and its connections.
- Add results to the plan of action and milestones and fix what you can before assessment.
- Retest critical findings and keep the evidence.
- Book your assessment only when evidence and remediation are in place.
Our guide to booking a C3PAO covers the assessment process, and compliance as a service for CMMC explains how to stay audit-ready over time.
Special Considerations for CUI Environments
- Data handling. Testers must follow CUI handling rules, and findings should never include unnecessary CUI.
- Personnel. Use testers who meet your contract and U.S. person requirements where they apply.
- Authorized tooling. Confirm that scanning and testing tools are approved for use in government cloud environments.
- Rules of engagement. Government cloud providers have their own testing policies.
- Reporting. Protect the report itself, because it describes your weaknesses.
How Often Should You Test?
At least annually, after significant changes to the CUI environment, and ahead of any assessment. Between engagements, regular vulnerability scanning and recurring external testing keep exposure in check, as discussed in PTaaS vs traditional penetration testing. For monitoring, see our guide to SIEM tools, managed SIEM and SOCaaS.
Common Findings in Defense Contractor Environments
Plan of Action and Milestones
Not every issue can be fixed before an assessment. CMMC allows limited use of a plan of action and milestones for certain requirements, with rules about what can be deferred and for how long, and those rules can change. Treat any open penetration test finding that affects a CMMC requirement as a potential plan-of-action item, document the owner, the date and the interim control, and confirm with your assessor what is acceptable. Critical findings affecting access control or boundary protection are better fixed than deferred.
Practical Tips for Small Defense Suppliers
- Shrink scope by creating a small, well-defined CUI enclave rather than treating the whole company as in scope.
- Use government-ready cloud services for CUI where appropriate, and understand the shared responsibility split.
- Prioritize MFA, patching, logging and access control before spending on advanced testing.
- Run a focused test on the enclave and its boundary, then expand as the program matures.
- Keep a single evidence folder that maps tests, fixes and retests to requirements.
Frequently Asked Questions
Is penetration testing required for CMMC Level 2?
CMMC Level 2 is based on NIST SP 800-171, which does not name penetration testing. It does require vulnerability scanning, risk assessments and periodic control assessments, and penetration testing is a common way to support them.
Does CMMC Level 3 require penetration testing?
Level 3 incorporates selected requirements from NIST SP 800-172, which includes penetration testing among its enhanced requirements. Confirm applicability with your contracting officer.
Will a C3PAO perform penetration testing?
A C3PAO assesses whether controls are implemented and effective by reviewing evidence, interviewing personnel and examining systems. It does not typically act as your penetration tester, so you should find issues yourself first.
What should CMMC penetration testing scope include?
The CUI enclave, its boundary and segmentation, external exposure, internal paths toward CUI, identity and access controls, cloud environments and monitoring.
How often should defense contractors run penetration tests?
At least annually and after significant changes to the CUI environment, plus before a formal assessment.
Can penetration testing replace a CMMC readiness assessment?
No. A readiness assessment checks all required practices against the standard. A penetration test checks whether controls withstand attack. You usually want both.
Final Thoughts
Even where it is not a named requirement, CMMC penetration testing gives you something no policy can: proof that your controls protect CUI under attack. Scope it around the enclave, fix what it finds and bring the evidence to your assessment.
Talk to Privaxi about CMMC compliance services and testing aligned to your assessment timeline.
Related Articles

Secure Your Business's Future
Contact us today for a personalized consultation and see how we can tailor a security solution that fits your business needs perfectly.
