
Financial Services Penetration Testing: Banks, Fintech & Credit Unions


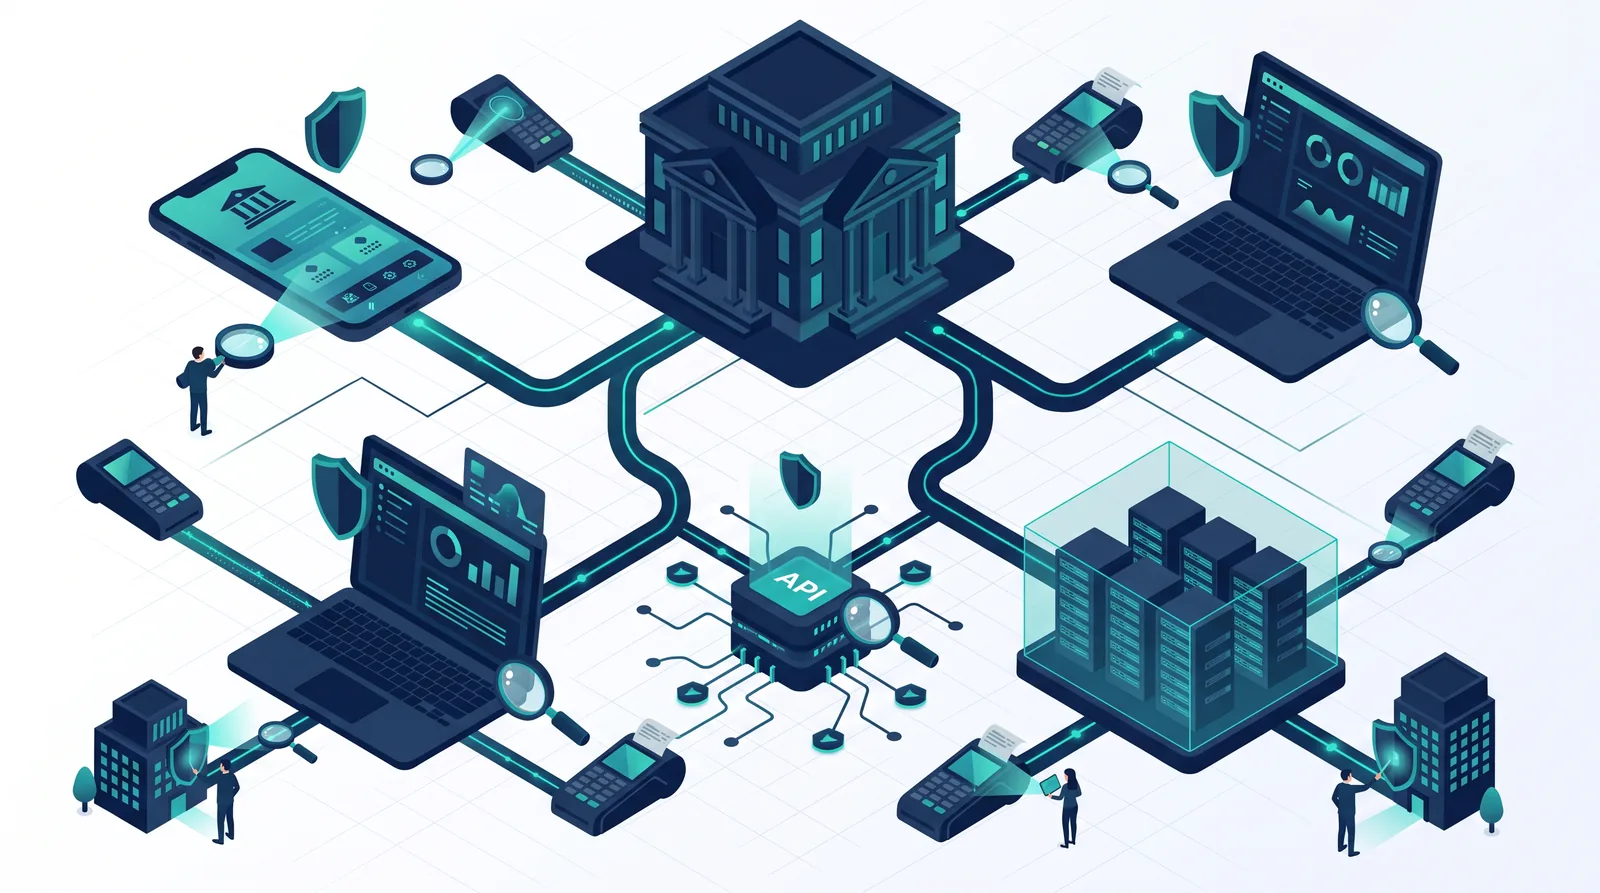
Quick answer: Financial services penetration testing is security testing designed around banks, credit unions, lenders, payment companies and fintechs. Regulators and partners expect regular testing: the FTC Safeguards Rule calls for annual penetration testing for covered non-bank institutions, NYDFS Part 500 requires it annually, and PCI DSS requires it for card data. Scope should center on customer-facing apps, APIs, payment flows and third-party integrations.
Financial institutions hold money, identities and trust, which makes them a constant target. They also operate under some of the most detailed security expectations of any industry, from federal safeguards rules to state regulations, card brand requirements and bank partner reviews.
This guide explains financial services penetration testing: the rules that drive it, what to test across banks, credit unions and fintechs, how often, and how to prepare for examiners and partners. For general services, see Privaxi's penetration testing services.
Why Financial Services Penetration Testing Is Different
- High-value targets. Fraud, account takeover and data theft pay well.
- Complex ecosystems. Core banking, digital banking, payment processors, card networks and fintech partners all connect through APIs.
- Regulatory scrutiny. Examiners and partner banks ask for evidence, not intentions.
- Customer trust. A single breach can end a relationship permanently.
- Speed of change. Fintech products release frequently, so yesterday's test ages quickly.
Regulatory Drivers for Penetration Testing in Finance
Requirements change, and your obligations depend on your charter, size and activities. Confirm specifics with your compliance counsel or examiner. For card data detail, see PCI DSS 11.4 penetration testing.
Financial Services Penetration Testing for Banks and Credit Unions
- Online and mobile banking. Authentication, session handling, transaction authorization and account takeover paths.
- APIs. Open banking and partner APIs, authorization and rate limiting.
- Network perimeter. VPN, remote access, email and exposed services.
- Internal network. Segmentation between corporate, branch, ATM and core systems.
- Core and payment connections. Interfaces to processors and card networks.
- Branch and endpoint security. Workstations, kiosks and wireless networks.
- Social engineering. Phishing and vishing resilience, within agreed limits.
The web application penetration testing and internal penetration testing guides explain what these tests involve.
Financial Services Penetration Testing for Fintech and Payments Companies
- Customer apps and dashboards, including role-based access and multi-tenant isolation.
- Payment flows and business logic, such as limits, refunds, reversals and double-spend conditions.
- KYC and onboarding. Document upload, identity verification and fraud controls.
- API keys and webhooks. Secret handling, signature validation and replay protection.
- Cloud infrastructure. Storage, identities and secrets. See AWS penetration testing.
- CI/CD and supply chain. Build pipelines, dependencies and deployment credentials.
Fintechs also benefit from the enterprise-oriented practices in SaaS penetration testing and the evidence expectations in SOC 2 penetration testing requirements.
Common Findings in Financial Services Environments
How Often Should Financial Services Penetration Testing Happen?
The baseline is at least annually and after significant changes, such as new products, core upgrades, major releases or vendor changes. Many institutions also run recurring external testing and vulnerability scanning between annual tests. See PTaaS vs traditional penetration testing for how to combine them, and consider monitoring through a managed SIEM.
How to Prepare for Examiners and Partner Reviews
- Keep the full evidence trail: scope, methodology, report, remediation log and retest results.
- Show independence. Use a qualified third party, not the team that built the system.
- Tie findings to your risk assessment and board or committee reporting.
- Document risk acceptances with owners and review dates.
- Prepare a shareable summary for partner banks and vendor questionnaires.
- Align with your incident response plan and test notification procedures.
Our guides to the penetration testing report and penetration testing remediation explain how to build that evidence.
Choosing a Provider for Financial Services Penetration Testing
Look for experience with financial applications and regulations, a documented penetration testing methodology, clear rules of engagement for production systems and the ability to produce reports that examiners and partners accept. See choosing a penetration testing company and how much penetration testing costs for what to ask.
Mobile Banking and Payment App Testing
Mobile apps add their own attack surface. Testers review how the app stores data on the device, how it communicates with APIs, whether it protects against tampering and whether authentication and device binding resist abuse. The OWASP Mobile Application Security Verification Standard (MASVS) is a common reference. Backend APIs matter just as much as the app itself, since attackers often bypass the interface and call the API directly.
Third-Party and Vendor Risk
Financial institutions rely on cores, processors, aggregators, identity providers and fintech partners, and each connection is a path for an attacker. Testing should examine how partner credentials are stored and scoped, what data flows through integrations, how webhooks are authenticated and whether a compromised partner could reach your systems. Regulators increasingly expect institutions to oversee vendors, and test evidence from your own environment complements vendor questionnaires.
Board and Committee Reporting
Boards and risk committees want clarity, not technical detail. Summarize results in terms of risk to customer funds, customer data, operations and regulatory standing, show trends across tests and report how quickly critical and high findings were fixed. A one-page dashboard with open findings by severity, time to remediate and next planned tests helps governance and satisfies examiners who ask how management oversees testing.
Questions to Ask a Financial Services Testing Provider
- Which financial regulations and frameworks do you map your reports to?
- Have you tested core banking integrations, payment flows and mobile apps?
- How do you handle production safety for systems that move money?
- Do you provide a summary letter suitable for examiners and sponsor banks?
- Is retesting included, and how quickly can it be scheduled?
Frequently Asked Questions
Is penetration testing required for banks and financial institutions?
Requirements depend on the regulator and institution type. NYDFS Part 500 and the FTC Safeguards Rule point to annual penetration testing for covered entities, PCI DSS requires it for card data, and federal examiners expect risk-based testing as part of an information security program.
How often should a bank or fintech perform penetration testing?
At least annually and after significant changes such as new products, major releases or infrastructure changes. Many also test the external perimeter more often.
What does the FTC Safeguards Rule say about penetration testing?
It calls for either continuous monitoring or annual penetration testing together with vulnerability assessments at least every six months, for covered non-bank financial institutions.
Do fintech startups need penetration testing?
Yes. Sponsor banks, enterprise customers and regulators expect it, and fintechs hold sensitive financial and identity data that attackers target.
What should a financial services penetration test cover?
Customer-facing applications, APIs, payment and transaction flows, authentication, network perimeter and internal segmentation, cloud infrastructure and third-party integrations.
Can financial institutions share penetration test reports with partners?
Usually under confidentiality agreements. Many share a summary letter instead of the full technical report.
Final Thoughts
Strong financial services penetration testing is regular, scoped to money movement and customer data, and documented so regulators and partners can rely on it. Test the paths that matter most, fix what you find and keep the evidence.
To scope testing for your institution, explore Privaxi's penetration testing services and request a consultation.
Related Articles

Secure Your Business's Future
Contact us today for a personalized consultation and see how we can tailor a security solution that fits your business needs perfectly.
