

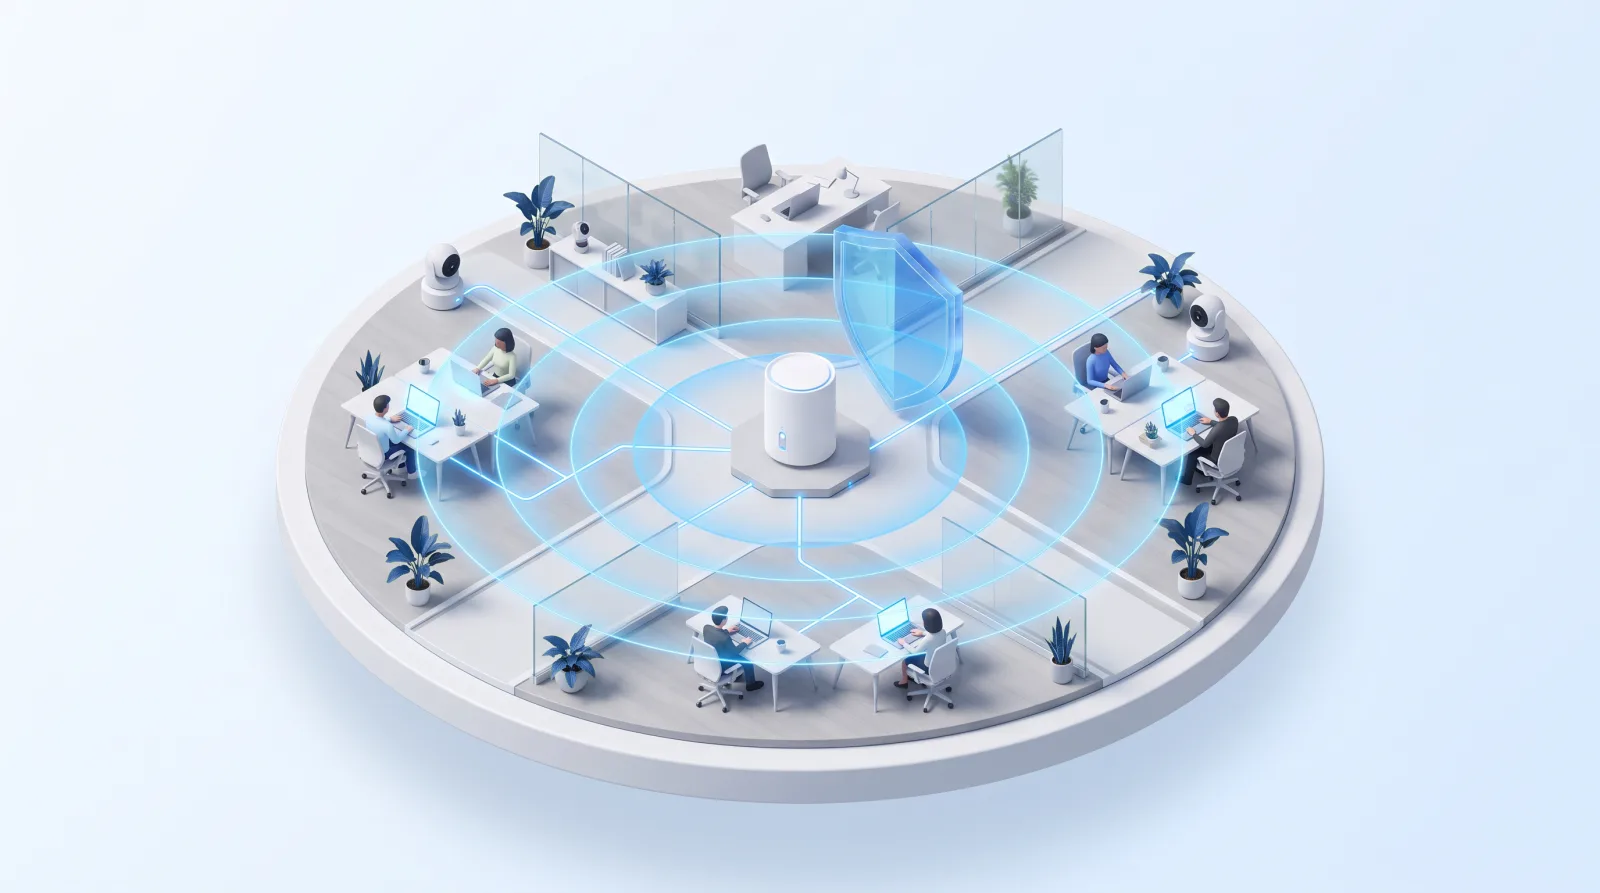
Wireless Penetration Testing: How to Secure Your Wi-Fi Networks



Quick answer: Wireless penetration testing is an authorized assessment of your Wi-Fi networks and related wireless technologies to find weaknesses in configuration, authentication, encryption and segmentation before attackers do. It checks whether corporate, guest and device networks are properly separated, whether strong authentication is enforced, whether unauthorized access points exist and whether wireless traffic can reach sensitive systems. The result is a prioritized list of fixes that make your wireless environment safer.
Wireless networks extend your perimeter beyond your walls. Signals reach parking lots, neighboring offices and public spaces, which means anyone nearby can try to connect. At the same time, offices, warehouses, hospitals, retail stores and factories depend on Wi-Fi for laptops, phones, scanners, cameras and connected devices. A single misconfigured network can undo the protection provided by firewalls and endpoint tools.
This guide explains what wireless penetration testing covers, why it matters, how engagements are planned, what common findings look like and how to fix them. To include wireless assessments in your security program, explore Privaxi's testing and assessment services.
What Is Wireless Penetration Testing?
Wireless penetration testing evaluates the security of wireless networks and the systems they connect to. Qualified testers work on site or with approved remote equipment to review how networks are configured, how users and devices authenticate, how traffic is separated and whether wireless access can lead to sensitive internal resources. The test is performed with written authorization and agreed limits so that business operations are not disrupted.
It is one part of a broader testing program. For an overview of the other test types, see our guide to types of penetration testing.
Why Wireless Security Matters
Signals do not stop at the wall: attackers can attempt access from outside your building.
Wireless often bypasses perimeter controls: a weak network can provide a path straight into internal systems.
Guest networks can be misconfigured: poor separation can expose corporate resources to visitors.
Connected devices are growing: printers, cameras, sensors and medical devices often use wireless and may have weak settings.
Rogue access points appear: employees or contractors may plug in unauthorized devices that bypass security.
Compliance expectations: frameworks such as PCI DSS require organizations to detect unauthorized wireless access points.
Regular wireless penetration testing helps you understand these risks and fix them before they are exploited.
What Wireless Penetration Testing Covers
| Area | What is reviewed | Why it matters |
|---|---|---|
| Corporate Wi-Fi | Authentication method, encryption, certificate validation and access policies | Protects employee devices and internal systems |
| Guest Wi-Fi | Isolation from corporate networks, client isolation and captive portal controls | Prevents visitors from reaching internal resources |
| Device and IoT networks | Separation, credentials and access to other segments | Limits the impact of weak device security |
| Segmentation | Firewall and VLAN rules between wireless and wired networks | Keeps sensitive environments isolated |
| Rogue and unauthorized access points | Detection of unapproved devices connected to the network | Stops hidden backdoors into your environment |
| Wireless infrastructure | Controller and access point management, firmware and admin access | Protects the systems that run the network |
| Signal coverage | How far networks reach beyond the premises | Helps reduce unnecessary exposure |
Some engagements also review other wireless technologies used by the business, such as Bluetooth devices or specialized industrial wireless systems, where they connect to sensitive operations.
How a Wireless Penetration Test Works
Planning and authorization: agree on locations, networks in scope, testing windows, contacts and safety limits.
Discovery: identify the organization's wireless networks and confirm which are in scope.
Configuration review: assess authentication, encryption and network settings against best practices.
Controlled testing: safely validate whether weaknesses could allow unauthorized access, within agreed rules.
Segmentation validation: confirm what an authorized or unauthorized wireless user could reach.
Rogue device checks: look for unapproved access points connected to the network.
Reporting: document findings, risk ratings and clear remediation steps.
Retesting: confirm fixes after changes are made.
This process aligns with recognized methodologies. For more detail, see our overview of penetration testing methodology.
Planning a Wireless Assessment
Wireless testing has some unique planning needs. Testers usually need physical presence near each site, so decide which locations matter most, such as headquarters, data centers, warehouses, clinics or retail stores. Provide floor plans, network diagrams, a list of approved access points and details of authentication systems. Agree on testing hours so that any impact on users is minimal, and inform building security so testers are not mistaken for intruders. Make sure only networks owned by your organization are tested. It also helps to list any critical wireless-dependent operations, such as warehouse scanners or clinical devices, so testers can take extra care around them and schedule sensitive checks outside peak hours. Our guide to penetration testing scope explains how to define clear boundaries.
Common Wireless Findings
Legacy or weak encryption settings still enabled for compatibility.
Shared passwords on corporate networks that are rarely changed and widely known.
Devices that do not validate server certificates during enterprise authentication.
Guest networks that can reach internal systems or management interfaces.
No client isolation on guest networks, allowing visitors to see each other's devices.
IoT and device networks with flat access to the corporate environment.
Unauthorized access points connected to internal switches.
Wireless controllers with default or weak administrative credentials.
Outdated access point firmware with known vulnerabilities.
Signal coverage extending far beyond the building.
Each of these findings is common, and most can be fixed with configuration changes rather than new hardware. Where hardware is very old, plan replacements as part of normal refresh cycles.
How to Fix Common Issues
Use modern encryption standards and retire legacy settings as soon as devices allow.
Use enterprise authentication with individual credentials or certificates for corporate networks.
Configure devices to validate server certificates during authentication.
Isolate guest networks completely from corporate resources and enable client isolation.
Place IoT and device networks in separate segments with strict firewall rules.
Deploy wireless intrusion detection or regular scans to find rogue access points.
Change default credentials and restrict management access to wireless infrastructure.
Keep access point and controller firmware up to date.
Tune signal strength to reduce coverage outside your premises.
After fixes are applied, retesting confirms they work. Our guide to penetration testing remediation explains how to prioritize and verify changes.
Wireless Testing and Compliance
Several frameworks address wireless security. PCI DSS requires organizations to test for unauthorized wireless access points at least every three months and to protect wireless networks connected to the cardholder data environment. HIPAA, SOC 2, ISO 27001 and NIST-based programs expect network security controls that include wireless. Findings and remediation evidence from wireless penetration testing help demonstrate these controls to auditors. For framework details, see our guides to PCI DSS 11.4 penetration testing and penetration testing compliance requirements.
Wireless Security by Industry
Healthcare: clinical devices, patient guest Wi-Fi and staff networks must be carefully separated. See HIPAA penetration testing.
Retail: payment terminals and store networks must be isolated from guest Wi-Fi. See ecommerce penetration testing.
Manufacturing and logistics: scanners, sensors and control systems often rely on wireless connections.
Financial services: branch networks and office Wi-Fi must protect sensitive customer data. See financial services penetration testing.
Offices and SaaS companies: employee devices, meeting rooms and guest access need clear separation.
How Often Should You Test?
Many organizations perform wireless penetration testing annually and after major changes, such as new offices, new wireless infrastructure or network redesigns. Rogue access point detection should run more often, and PCI DSS requires it at least quarterly for in-scope environments. Organizations with many locations often rotate testing across sites each year. For overall testing cadence, see annual penetration testing.
Combining Wireless Testing With Other Tests
Wireless access is often the first step in a larger attack path. Pairing wireless testing with internal penetration testing shows what an attacker could reach after connecting. Pairing it with physical penetration testing shows whether someone could get close enough to plug in an unauthorized device. For a full view of network risk, see network penetration testing.
Choosing a Wireless Testing Provider
Experience with enterprise wireless platforms and authentication systems.
Ability to test multiple sites efficiently.
Clear rules of engagement that avoid disrupting users.
Reports with practical configuration fixes, not just tool output.
Retesting included to confirm changes.
Experience with industry-specific devices and compliance needs.
Our guide to choosing a penetration testing company lists more questions to ask.
Cost of Wireless Penetration Testing
The cost of wireless penetration testing depends on the number of sites, the number of networks and access points, travel requirements, the size of each location and whether segmentation testing and retesting are included. Multi-site organizations can reduce costs by testing representative locations and applying fixes across all sites. Bundling wireless testing with internal testing during the same visit also saves travel time. For general pricing factors, see penetration testing cost.
Common Mistakes to Avoid
Testing only the corporate network and ignoring guest and device networks.
Assuming a strong password alone makes Wi-Fi secure.
Leaving legacy settings enabled indefinitely for old devices.
Skipping segmentation checks between wireless and sensitive systems.
Never checking for rogue access points.
Not retesting after configuration changes.
Building a Secure Wireless Program
A single test is only a snapshot. Strong wireless security combines regular wireless penetration testing with continuous monitoring for rogue devices, documented configuration standards, change management for new access points and clear ownership of wireless infrastructure. Include wireless in your asset inventory, review guest network policies regularly and plan device replacements so legacy settings can be retired. Over time, this turns wireless from a hidden risk into a well-managed part of your network.
Preparing Your Team for Testing
Name a site contact at each location who can give testers access and answer questions.
Share a list of approved networks, access points and controllers so unauthorized devices are easy to spot.
Provide test accounts for corporate and guest networks where authenticated testing is in scope.
Inform facilities and building security about the testing schedule.
Agree how urgent findings, such as an exposed management interface, will be reported during testing.
Reserve time after the test for configuration changes and a retest.
Good preparation shortens time on site, reduces cost and produces clearer results for every location in scope.
Remote Work and Wireless Risk
Wireless risk does not end at the office. Employees connect from home networks, hotels, airports and cafes that your organization does not control. While these networks are usually outside the scope of wireless penetration testing, the test results should inform your remote work policies. Make sure company devices use a VPN or zero trust access, keep endpoint protection up to date, prefer phishing-resistant multi-factor authentication and avoid automatic connection to open networks. Combining strong office wireless security with sensible device policies gives employees a safer experience wherever they work.
Frequently Asked Questions About Wireless Penetration Testing
What is wireless penetration testing?
Wireless penetration testing is an authorized assessment of Wi-Fi and related wireless technologies to find weaknesses in configuration, authentication, encryption and segmentation.
Does wireless testing need to be on site?
Usually yes. Testers need to be within range of the networks, either in person or using approved remote equipment placed at the site.
Will wireless testing disrupt users?
A well-planned test is designed to avoid disruption, with agreed testing windows and safety limits in the rules of engagement.
Does PCI DSS require wireless testing?
PCI DSS requires organizations to test for unauthorized wireless access points at least every three months and to secure wireless networks connected to cardholder data.
What are the most common wireless findings?
Weak or legacy encryption, shared passwords, poor guest network isolation, flat device networks, rogue access points and outdated firmware.
How often should wireless networks be tested?
Annually and after major changes, with more frequent checks for rogue access points.
Final Thoughts
Wireless penetration testing shows whether your Wi-Fi networks protect the systems and data behind them. Test corporate, guest and device networks, validate segmentation, look for rogue access points, fix the issues you find and retest to confirm the changes work.
To plan wireless penetration testing for your offices and sites, explore Privaxi's testing and assessment services.
Related Articles


Secure Your Business's Future
Contact us today for a personalized consultation and see how we can tailor a security solution that fits your business needs perfectly.
