

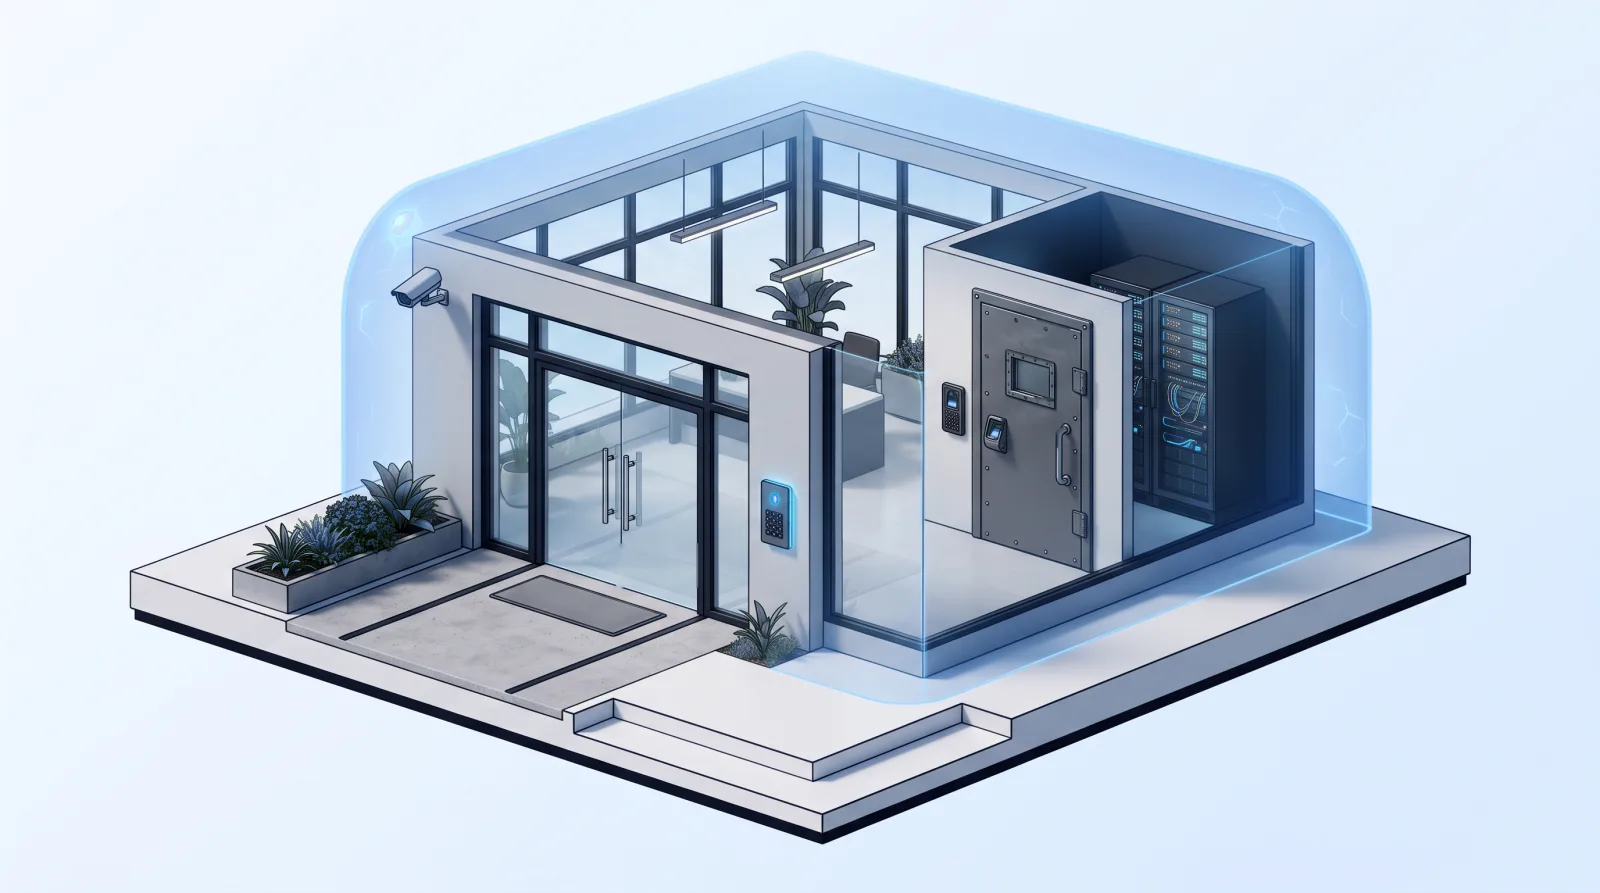
Physical Penetration Testing: Protecting Facilities, Devices and Data



Quick answer: Physical penetration testing is an authorized assessment of how well your buildings, offices, data centers and other facilities protect people, equipment and data from unauthorized access. It reviews controls such as reception and visitor management, badge systems, locks, cameras, alarms, secure areas and staff awareness, then reports gaps and practical fixes. It is always run with written approval from the right leaders, clear limits and a focus on safety.
Cybersecurity programs often focus on networks and applications, but physical access can bypass many digital controls. Someone who reaches an unlocked server room, an unattended laptop, an open network port or a printer full of sensitive documents may not need to break through a firewall at all. Physical and digital security work together, and a weakness in one can undermine the other.
This guide explains what physical penetration testing covers, why organizations use it, how engagements are planned safely, what common findings look like and how to improve. To include physical assessments in your security program, explore Privaxi's testing and assessment services.
What Is Physical Penetration Testing?
Physical penetration testing evaluates whether physical security controls prevent, detect and respond to unauthorized access attempts. Qualified assessors, working under written authorization and agreed rules, check whether facilities can be entered, whether restricted areas stay restricted, whether staff follow procedures and whether security teams notice and respond. The goal is to find gaps before a real intruder does.
It is one of several test types in a complete security program. For an overview, see our guide to types of penetration testing.
Why Physical Security Matters for Cybersecurity
Direct access to systems: physical access to servers, network equipment or workstations can bypass many technical controls.
Theft of devices and data: laptops, drives and printed documents can be removed from poorly controlled areas.
Unauthorized devices: unknown equipment connected to internal networks can provide remote access.
Regulatory expectations: frameworks such as PCI DSS, HIPAA and ISO 27001 include physical security requirements.
Safety of people: strong access control also protects employees, visitors and customers.
Incident response: testing shows whether guards, reception and security teams respond correctly.
Combining physical penetration testing with technical testing gives a more complete picture of real-world risk.
What Physical Assessments Can Cover
| Area | What is reviewed | Typical improvement |
|---|---|---|
| Perimeter | Fences, gates, parking areas, lighting and external doors | Better lighting, secured gates and door monitoring |
| Reception and visitor management | Sign-in, identity checks, escorts and visitor badges | Stronger visitor procedures and escort rules |
| Access control systems | Badge readers, door configurations and access permissions | Access reviews and correct door hardware settings |
| Secure areas | Server rooms, data centers, network closets and records rooms | Stricter access lists and monitoring |
| Monitoring and alarms | Camera coverage, alarm response and guard procedures | Coverage improvements and response drills |
| Workspace security | Clean desk practices, screen locking and document disposal | Policies, secure shredding and awareness |
| Staff awareness | Whether staff challenge unknown people and report concerns | Training and clear reporting channels |
Scope should match your risks. A company with a single office may focus on reception, server rooms and workspace security, while a data center operator will review multiple layers of physical protection.
How a Physical Engagement Works
Define objectives: decide what you want to learn, such as whether restricted areas are protected or whether staff report unknown visitors.
Get authorization: obtain written approval from leaders who have authority over each site, including landlords or building management where needed.
Agree rules of engagement: set locations, dates, times, permitted activities, prohibited activities and emergency contacts.
Plan for safety: confirm that nothing will damage property, endanger people or trigger unsafe responses.
Review and observe: assessors evaluate controls, procedures and staff responses within agreed limits.
Document evidence: record findings with photos or notes where allowed, without collecting sensitive data unnecessarily.
Report: deliver findings, risk ratings and practical recommendations.
Improve and retest: fix gaps and verify changes.
Each assessor carries a signed authorization letter and the contact details of an approved internal contact who can confirm the engagement at any time. This protects everyone involved. For general methodology, see penetration testing methodology.
Safety, Legal and Ethical Considerations
Only test sites your organization owns or has explicit permission to test, and include landlords or shared building managers where relevant.
Never allow activities that could damage property or put people at risk.
Agree how assessors will identify themselves if challenged, and make sure the authorization can be verified quickly.
Avoid collecting personal data or sensitive documents beyond what is needed to prove a finding.
Coordinate with legal counsel and, where appropriate, HR.
Do not use results to discipline individual employees; focus on processes and controls.
A responsible physical penetration testing provider treats safety and legality as the first priority in every engagement.
Common Findings
Doors propped open or not closing fully, especially at loading areas and side entrances.
Visitors able to move through buildings without escorts or visible badges.
Server rooms and network closets with broad access lists or unlocked doors.
Badge access permissions that were never removed after role changes or departures.
Camera blind spots near sensitive areas.
Unattended, unlocked workstations and sensitive documents left on desks or printers.
Network ports in public or meeting areas connected to internal networks.
Staff who are unsure whether or how to challenge unknown people.
Alarm alerts that are not investigated quickly.
Most of these findings are inexpensive to fix once identified. That is why physical penetration testing often delivers high value for a modest investment.
How to Fix Common Issues
Install door closers and door-ajar alarms on sensitive entrances.
Enforce visitor sign-in, identity checks, visible badges and escorts.
Review badge access lists regularly and remove access promptly when people leave or change roles.
Restrict server room and network closet access to a small, approved group, and log entries.
Improve camera coverage and make sure footage is reviewed when alerts occur.
Enforce screen locking, clean desk practices and secure document disposal.
Disable unused network ports and apply network access control in public areas.
Train staff on how to politely challenge unknown people and how to report concerns.
Run response drills with security teams and reception.
For a structured approach to closing gaps, read our guide to penetration testing remediation.
Physical Security and Compliance
Many frameworks include physical security requirements. PCI DSS Requirement 9 addresses restricting physical access to cardholder data. The HIPAA Security Rule includes physical safeguards for facilities and workstations. ISO 27001 Annex A includes a set of physical controls covering perimeters, entry, secure areas and equipment. SOC 2 and HITRUST also evaluate physical access controls. Evidence from physical penetration testing helps show auditors that these controls work in practice. For framework details, see penetration testing compliance requirements.
Connecting Physical and Technical Testing
Physical access is often only the first step. If someone could reach an internal network port or unattended workstation, what could they do next? Pairing physical assessments with internal penetration testing and wireless penetration testing shows the full attack path. Pairing them with social engineering penetration testing shows how people and processes respond. For a broader adversary simulation, see red teaming and penetration testing.
Physical Security by Industry
Healthcare: clinics and hospitals must protect patient records, medical devices and restricted areas while staying open to the public. See HIPAA penetration testing.
Financial services: branches, offices and data rooms hold sensitive customer data. See financial services penetration testing.
Retail: stores must protect payment terminals, back offices and network equipment.
Data centers and hosting: layered physical controls are central to customer trust.
Government and defense: facilities handling sensitive information often face strict physical requirements. See government penetration testing.
How Often Should You Test?
Many organizations perform physical penetration testing annually for critical sites and after major changes, such as office moves, new data centers, renovations or new access control systems. Organizations with many locations often rotate assessments across sites. Smaller checks, such as reviewing badge access lists and walking through clean desk practices, can happen more often. For overall testing cadence, see annual penetration testing.
Choosing a Provider
Strong safety, legal and ethical practices.
Experience with your type of facility and industry.
Clear authorization process and rules of engagement.
Reports that focus on controls and processes, with practical fixes.
Ability to combine physical findings with technical testing.
Discretion and secure handling of evidence.
Our guide to choosing a penetration testing company lists more questions to ask.
Cost of Physical Penetration Testing
The cost of physical penetration testing depends on the number and size of sites, travel requirements, the areas in scope, the depth of the assessment and whether it is combined with technical or social engineering testing. Testing a representative site and applying improvements across similar locations can reduce cost. Combining several nearby sites into one visit also reduces travel costs. For general pricing factors, see penetration testing cost.
Preparing for an Assessment
Name an executive sponsor and an on-call contact for each site.
Confirm ownership and permissions for every building and area in scope.
Share floor plans and a list of sensitive areas.
Decide whether security staff and reception will be informed in advance.
Agree on how findings needing urgent action will be communicated.
Plan time for improvements and a follow-up review.
Common Mistakes to Avoid
Testing without written authorization from everyone who controls the site.
Focusing only on the front door while side entrances and loading areas stay untested.
Ignoring network ports and devices in public or shared areas.
Blaming individuals instead of improving procedures and training.
Not reviewing badge access permissions after the test.
Failing to retest after improvements.
Building a Long-Term Physical Security Program
A single assessment is a snapshot. Lasting improvement comes from combining regular physical penetration testing with everyday habits and clear ownership. Assign an owner for physical security at each site, keep an up-to-date inventory of secure areas and network equipment, and review badge access permissions at least quarterly. Connect your access control, camera and alarm systems to your security monitoring so suspicious activity is visible to the same team that watches for digital threats. Include physical scenarios in incident response exercises, and make sure reception, facilities and IT know who to call when something looks wrong.
Track a small set of metrics over time, such as the number of open physical findings, the time taken to remove access for departing staff and the results of clean desk walkthroughs. Share progress with leadership alongside your technical security metrics. When physical and digital security are managed as one program, gaps are easier to spot, fixes happen faster and the organization is better protected against attackers who look for the easiest way in.
Frequently Asked Questions About Physical Penetration Testing
What is physical penetration testing?
Physical penetration testing is an authorized assessment of how well buildings and facilities prevent, detect and respond to unauthorized access to people, equipment and data.
Is physical penetration testing legal?
Yes, when it is authorized in writing by everyone with authority over the site, follows agreed rules of engagement and prioritizes safety.
What areas are usually tested?
Perimeters, reception and visitor management, access control systems, secure areas such as server rooms, monitoring and alarms, workspace security and staff awareness.
Why does physical security matter for cybersecurity?
Physical access to devices, network equipment or documents can bypass many technical controls, so physical and digital security must work together.
Does compliance require physical security testing?
Frameworks such as PCI DSS, HIPAA, ISO 27001, SOC 2 and HITRUST include physical security requirements, and testing helps show those controls work.
How often should physical security be assessed?
Annually for critical sites and after major changes such as office moves, renovations or new access control systems.
Final Thoughts
Physical penetration testing shows whether your facilities protect the people, devices and data inside them. Run it with clear authorization and safety rules, focus on controls and processes, fix the gaps you find and combine results with technical testing for a complete view of risk.
To plan physical penetration testing for your offices and facilities, explore Privaxi's testing and assessment services.
Related Articles

Secure Your Business's Future
Contact us today for a personalized consultation and see how we can tailor a security solution that fits your business needs perfectly.
