
Red Team vs Penetration Testing: Differences & Which to Choose


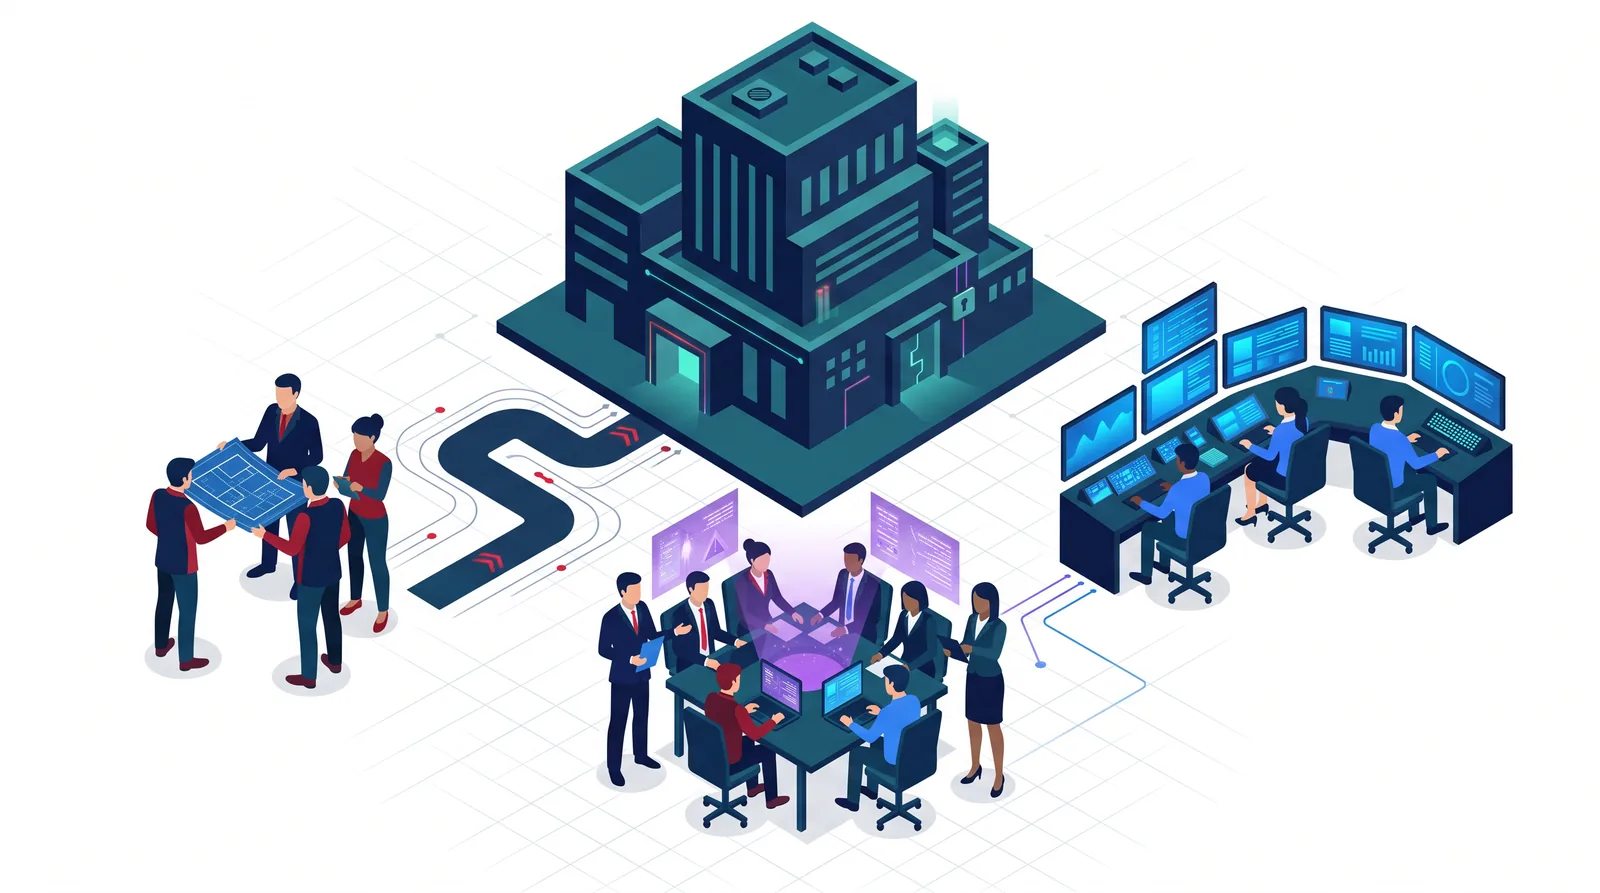
Quick answer: In the red team vs penetration testing comparison, a penetration test looks for as many exploitable weaknesses as possible within a defined scope, usually in days or weeks. A red team engagement simulates a real adversary pursuing a specific goal, often over weeks, while testing whether your people and detection tools notice. Most organizations should start with penetration testing and add red teaming once basic controls and monitoring are mature.
In red team vs penetration testing discussions, the terms get used interchangeably, but they are different exercises with different goals and different prices. Buying the wrong one means paying for a sophisticated simulation that finds issues you already knew about, or paying for a basic test and expecting it to prove you can detect a determined attacker.
This guide explains red team vs penetration testing: what each does, how they differ, when each makes sense and how purple teaming fits in. If you need testing today, see Privaxi's penetration testing services.
What Is Penetration Testing?
Penetration testing is a time-boxed, scoped assessment that aims to find and prove as many exploitable vulnerabilities as possible in specific systems. Testers are usually allowed to be noisy. Your security team may know it is happening. The deliverable is a prioritized list of findings and fixes. Our penetration testing methodology guide covers the process.
What Is a Red Team Assessment?
A red team assessment, sometimes called adversary simulation, imitates a real attacker pursuing an objective, such as stealing a specific dataset, reaching a critical system or demonstrating the ability to disrupt operations. The red team tries to avoid detection, uses multiple attack paths and can combine technical, physical and social engineering techniques within agreed limits.
The point is not to list every weakness. It is to test your whole defense: prevention, detection and response.
Red Team vs Penetration Testing: Key Differences
What About Blue Teams and Purple Teams?
The blue team is your defense: the analysts and tools that detect and respond to attacks. A red team exercise tests the blue team. A purple team exercise puts both on the same side. The red team runs specific techniques while the blue team watches, tunes detections and fills gaps in real time. It is often the most cost-effective way to improve detection, especially for organizations new to adversary simulation.
Red Team vs Penetration Testing: When Penetration Testing Is the Right Choice
- You need compliance evidence for PCI DSS, SOC 2, ISO 27001, HITRUST or HIPAA.
- You are testing a new application or major release.
- You have never had a test, or have not tested in the last year.
- You want a broad list of vulnerabilities to fix.
- Your budget or security team size is limited.
If you are unsure, start here. Read do I need a penetration test and our penetration testing scope guide.
Red Team vs Penetration Testing: When a Red Team Makes Sense
- You already run regular penetration tests and fix findings promptly.
- You have logging, monitoring and an incident response process, such as a SOC or a managed SIEM.
- You need to know whether you would detect and stop a determined attacker.
- Leadership or a regulator wants assurance beyond vulnerability lists.
- You hold high-value targets such as financial systems, health data or critical infrastructure.
What You Need Before a Red Team Engagement
- A tested baseline. If an ordinary test still finds critical issues, a red team will find them too, at much higher cost.
- Detection capability. Without logging and monitoring there is nothing to measure.
- An incident response plan. You need to know who responds and how.
- Clear objectives. For example, access to a particular database or production environment.
- Rules of engagement. Define off-limits systems, safety stops, emergency contacts and legal authorization.
- An executive sponsor who can approve the exercise and handle any real incident it triggers.
Breach and Attack Simulation vs Red Teaming
Breach and attack simulation (BAS) tools automatically replay known attacker techniques to check whether your controls detect or block them. They are repeatable and cheap to run, and they complement human-led exercises. They do not replace a creative human adversary who adapts to what they find.
A Practical Maturity Path
- Baseline: vulnerability scanning and an annual penetration test.
- Broaden: add internal and external testing and cloud assessments such as AWS penetration testing.
- Continuous: add recurring external testing, as described in PTaaS vs traditional penetration testing.
- Detect: build monitoring and response capability.
- Purple team: tune detections against realistic techniques.
- Red team: test the whole defense against an objective-driven adversary.
How to Choose a Provider
Ask whether the provider has experience in adversary simulation, how it handles safety and legal authorization, which frameworks it uses to describe attacker behavior, and whether it offers purple team workshops and a debrief with your defenders. Our guide to choosing a penetration testing company lists further questions, and the penetration testing report guide shows what good deliverables look like.
Example Red Team Objectives
- Obtain access to a defined sensitive dataset, such as customer records or source code.
- Gain administrative control of the corporate identity system and show that backups are reachable.
- Demonstrate the ability to reach a production environment from a corporate laptop.
- Show that a payment or approval workflow can be manipulated without triggering alerts.
- Maintain undetected access for a defined period to measure dwell time.
Objectives are written as outcomes the business cares about, not as technical checklists. They also define what counts as success, which keeps the engagement focused and easier to explain to executives.
What You Receive at the End of a Red Team Engagement
- An attack narrative showing the steps taken, the order and the timing.
- A detection timeline comparing red team actions with alerts your defenders saw.
- Gaps in prevention, detection and response, ranked by importance.
- Recommendations for technical fixes, process changes and training.
- A debrief workshop where red and blue teams walk through the exercise together.
- A re-run plan to test improvements later.
Legal, Safety and Trust Considerations
Because red team exercises are stealthy and broad, they need careful governance. Senior leadership must authorize them in writing, a small trusted group should know the exercise exists, and there should be an emergency stop and a way to tell the difference between the exercise and a real attack. Physical and social engineering elements require explicit legal review. Third-party systems, such as cloud providers and vendors, usually have their own testing rules and may need to be excluded or notified.
Frequently Asked Questions
What is the difference in red team vs penetration testing?
Penetration testing finds as many exploitable vulnerabilities as possible in a defined scope. Red teaming simulates a real adversary pursuing a specific goal over a longer period and tests detection and response as well as prevention.
Is a red team better than a penetration test?
Not inherently. They answer different questions. A penetration test is better for finding and fixing vulnerabilities and meeting compliance needs. A red team is better for testing whether a mature defense can detect and stop an attacker.
What is a purple team?
A purple team exercise combines red and blue teams collaboratively. The red team runs techniques while the blue team observes, tunes detection and closes gaps in real time.
How long does a red team engagement last?
Typically several weeks to a few months, depending on objectives and scope, because stealth and persistence take time.
Do compliance frameworks require red teaming?
Most frameworks require or expect penetration testing and vulnerability management, not red teaming. Some regulated sectors encourage adversary simulation for mature organizations.
Should a small business do a red team exercise?
Usually not first. Start with penetration testing and basic monitoring, then consider red or purple team exercises as your security program matures.
Final Thoughts
The honest answer to red team vs penetration testing is that they are steps on one path. Fix vulnerabilities with penetration tests, build detection and response, then use purple and red team exercises to prove the defense works.
Talk to Privaxi about where you are on that path. Our penetration testing services are the right starting point for most organizations.
Related Articles


Secure Your Business's Future
Contact us today for a personalized consultation and see how we can tailor a security solution that fits your business needs perfectly.
